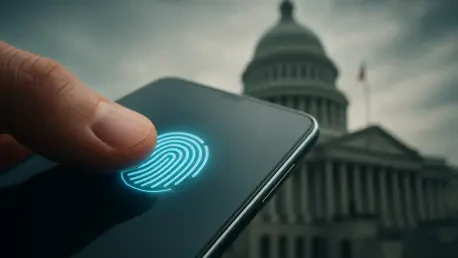
The tactile satisfaction of flipping through a leather wallet to find a plastic driver’s license is rapidly becoming a relic of a bygone analog era as state governments embrace the efficiency of biometric smartphone authentication. This movement is not merely a technological upgrade but a fundamental reimagining of how the state interacts with its residents. In the current landscape of 2026, the concept of a “digital front door” has evolved from a futuristic ambition into a functional necessity. State leaders across the country are grappling with a paradox: while the private sector has normalized instantaneous, secure digital transactions, many public institutions still rely on fragmented, agency-specific portals that frustrate users and invite security risks. The push toward centralization aims to bridge this gap, creating a unified experience that reflects the demands of a mobile-first society.
The sheer volume of digital interactions handled by state governments today necessitates a shift away from the traditional, physical methods of identity verification. For decades, a citizen’s relationship with the government was defined by a physical presence at a local office or the mailing of paper documents. However, as 2026 progresses, 22 states and Puerto Rico have already transitioned to mobile driver’s licenses (mDLs) and digital credentials. This evolution is driven by a desire to simplify the “patchwork” of government logins that previously required residents to maintain dozens of usernames and passwords for different services. Whether a person is applying for a fishing license, checking unemployment benefits, or renewing a professional certification, the goal is now a single, secure entry point that validates who they are across the entire state enterprise.
This modernization effort is heavily influenced by the seamless experiences provided by private-sector apps in the banking and retail industries. Residents no longer differentiate between the convenience of a commercial service and the services provided by their state government. They expect the same level of intuitive design and immediate response when interacting with public agencies. Consequently, state technology leaders are moving toward platforms that prioritize the resident experience (RX) rather than agency-centric administrative logic. This shift represents the death of the physical wallet as the primary repository of trust, replacing it with encrypted, state-verified digital tokens that provide greater privacy and utility for the modern citizen.
The Death of the Physical Wallet and the Rise of the Digital Front Door
The transition from plastic credentials to secure mobile wallets represents one of the most visible changes in the current administrative landscape. In the past, the physical driver’s license was the undisputed gold standard for identity verification, but it was inherently limited by its physical nature—vulnerable to loss, theft, and counterfeiting. Today, in 2026, mobile credentials offer a more secure and flexible alternative, allowing residents to share only the specific information required for a transaction. For example, a resident proving they are of legal age at a venue no longer needs to reveal their home address or exact birth date; the digital credential simply provides a verified “yes” or “no” through a cryptographically signed exchange. This privacy-preserving feature is a cornerstone of the new digital identity frameworks being deployed across the country.
Furthermore, the “patchwork” of government logins is finally being dismantled in favor of integrated systems. Historically, a resident might have one set of credentials for the Department of Motor Vehicles and an entirely different account for the Department of Revenue. This fragmentation was not only a nuisance for the public but also a significant security vulnerability, as users often reused weak passwords across multiple platforms. By centralizing these identities into a single “digital front door,” states are significantly reducing the friction associated with government interactions. This unified approach ensures that once a resident is authenticated, they can move seamlessly between different agency services without the need for redundant logins, mirroring the single sign-on experiences common in the enterprise software world.
The growing expectation for government services to mirror the seamless experience of private-sector apps has forced a change in how states design their digital infrastructure. High-performing states are no longer content with simply putting paper forms online; they are building sophisticated portals that anticipate user needs. The current trend emphasizes the use of biometric authentication, such as facial recognition or fingerprint scanning, to replace traditional passwords. This not only enhances security but also aligns with how residents already interact with their personal devices. As state governments adopt these private-sector standards, they are effectively turning the state portal into a high-utility app that resides in the pocket of every resident, making the government more accessible and responsive than ever before.
Why Identity Is Becoming the Cornerstone of Modern Governance
The urgency to combat sophisticated fraud and identity theft has never been higher than it is in 2026. Public programs, particularly those involved in distributing financial benefits, have become prime targets for organized cybercrime syndicates using synthetic identities and automated bots. Traditional methods of identity verification, which relied on static information like Social Security numbers, have proven insufficient in an era of massive data breaches. Modern governance now recognizes that a robust digital identity system is the first and most critical line of defense. By implementing real-time identity assurance that utilizes multi-factor authentication and verified state records, agencies can ensure that benefits reach the intended recipients while shutting the door on fraudulent actors.
Moreover, the historical inefficiency of agency silos is being addressed through a new lens of fiscal responsibility. For years, individual departments wasted taxpayer dollars by building and maintaining redundant identity systems, each with its own procurement process, security protocols, and support staff. This fragmented model led to “identity sprawl,” where a single resident’s data was duplicated and often inconsistent across multiple databases. In the current fiscal environment, state CIOs are championing centralization as a way to achieve economies of scale. By treating identity as a shared utility across the entire state government, leaders can redirect millions of dollars from redundant IT maintenance toward improving the quality and reach of actual public services.
The shift from paper-based verification to real-time digital assurance is also transforming the speed of government operations. In the legacy model, verifying a resident’s eligibility for a program often involved manual reviews of scanned documents, a process that could take weeks and was prone to human error. With the centralized digital identity systems being perfected between 2026 and 2028, these checks happen instantaneously. When a resident logs in, the system can automatically query verified data sources to confirm identity, residency, and eligibility status. This transition to real-time verification not only improves the resident experience by providing immediate results but also enhances the integrity of public programs by ensuring that every transaction is backed by a current, verified credential.
Strategic Frameworks: Centralization vs. Federated Models
In the pursuit of a unified resident experience, states are generally following one of two paths: total centralization or a hybrid federated model. The “Power of One” philosophy is best exemplified by states like Ohio and Washington, which are building “single entity” experiences. In Ohio, the “InnovateOhio Platform” serves as the foundational layer for all digital interactions, ensuring that the government feels like a single, cohesive organization to the resident. Washington state is currently executing a four-year strategic plan, running through 2029, to evolve its resident portal into a comprehensive hub. These states believe that a central identity authority is the most effective way to enforce security standards and provide a frictionless user journey, effectively removing the bureaucratic walls that once separated different state functions.
In contrast, the hybrid alternative provides a path for states that need to balance centralized standards with agency autonomy. New York’s approach reflects this middle ground, acknowledging that while certain agencies have unique legal or functional requirements, they should still benefit from a common infrastructure. In this federated model, the central IT office provides the “plumbing”—the underlying identity verification tools and security protocols—while individual agencies maintain control over their specific service delivery. This allows for a more flexible implementation that can be tailored to the diverse needs of large, complex state bureaucracies. This hybrid model often proves more palatable in political environments where agency leaders are wary of ceding too much control to a central technology office.
National alignment is also playing a significant role in how states shape their digital identity strategies, particularly through the influence of federal standards. The expansion of Login.gov as a universal sign-on for federal services has provided a blueprint for state-level initiatives. Many states are now looking to align their own identity assurance levels with the National Institute of Standards and Technology (NIST) guidelines to ensure interoperability across different levels of government. This alignment is crucial for programs that involve both state and federal cooperation, such as Medicaid or disaster relief. By adopting these common standards, states are not only improving their own security posture but also contributing to a broader national ecosystem where a single digital identity could eventually facilitate secure interactions with any government entity.
Expert Perspectives on Overcoming Implementation Hurdles
Implementing a centralized digital identity system is as much a challenge of strategy as it is of technology. Expert CISOs, particularly in large states like California, often favor a “bite-sized” approach to scaling these tools. Rather than attempting a massive “big bang” rollout that covers every agency at once, the strategy involves identifying specific, high-impact business use cases to serve as a proof-of-concept. For instance, California has utilized its centralized identity tools to manage specific legal requirements, such as data request opt-outs for privacy protection. By proving the value of the system in a controlled environment, technology leaders can build the necessary trust and momentum to expand the system to more complex areas like healthcare or taxation without overwhelming the state’s technical capacity.
Insights from the National Association of State Chief Information Officers (NASCIO) highlight that the transition to enterprise-level utilities is often hampered by significant fiscal and organizational barriers. According to recent research, approximately 70% of state technology leaders cite inadequate funding as a primary obstacle to modernizing identity systems. Building a secure, resilient infrastructure requires long-term investment that doesn’t always fit neatly into traditional two-year budget cycles. Furthermore, about 68% of CIOs identify cultural resistance as a major hurdle. Agencies that have historically operated with total independence are often reluctant to adopt centralized tools, fearing a loss of control over their data or a reduction in their departmental relevance.
Breaking this silo mentality requires strong executive leadership and a fundamental shift in institutional culture. Washington state’s CIO, Bill Kehoe, has emphasized that the greatest challenge is not the software, but the mindset of the bureaucracy. Moving from an “agency-centric” logic to a “resident-centric” design requires constant communication and a clear demonstration of the benefits for both the agency and the public. When agency leaders see that centralized identity management reduces their own administrative burden and improves their security profile, they are more likely to become champions of the enterprise approach. Overcoming this resistance is a long-term process that involves a combination of executive mandates, collaborative governance, and the proven success of early adopters.
Roadmap for a Successful Digital Identity Transition
A successful transition to a centralized digital identity system must begin with a commitment to resident-centric design. This means moving away from portals organized by the internal structure of the government and toward interfaces designed around the life events of the resident. For example, if a resident moves to a new city, they should be able to update their address once and have that change propagate across the DMV, the voter registration office, and their professional licensing boards automatically. By prioritizing how the resident actually interacts with services, states can create a “digital front door” that feels helpful rather than bureaucratic. This approach requires deep collaboration between UX designers and policy experts to ensure that legal requirements are met without sacrificing the simplicity of the user interface.
Securing sustainable funding is another critical element of the roadmap for the years 2026 through 2030. Because digital identity is foundational infrastructure, it cannot be treated as a one-off project funded by temporary grants. States must find ways to integrate these costs into their recurring budgets or develop charge-back models where agencies pay a small fee for each identity verification performed by the central system. This ensures that the platform can be continuously updated to defend against emerging cyber threats and to incorporate new features like blockchain-based credentials or advanced biometric checks. Without a long-term fiscal strategy, even the most sophisticated identity systems risk becoming obsolete or vulnerable as technology and threat landscapes evolve.
To build trust and demonstrate immediate value, states should start with high-impact use cases that provide a clear proof-of-concept. Identifying services that suffer from high fraud rates or significant administrative backlogs—such as unemployment insurance or professional licensing—provides an ideal testing ground for centralized identity tools. When these projects succeed in reducing fraud or speeding up processing times, they provide the political capital needed to secure broader adoption across the state government. Finally, establishing unified security and privacy protocols is non-negotiable. Residents must have total confidence that their data is protected and that they have control over how their information is shared. Transparent privacy policies and rigorous compliance with standards like NIST are the only ways to maintain the public trust necessary for a digital identity system to flourish.
The transition toward a unified digital identity framework represented the most significant shift in public administration in decades. It was no longer a question of whether states would modernize, but how effectively they managed the human and technical elements of that change. Leaders who prioritized the resident experience over agency silos successfully laid the groundwork for a more resilient and responsive government. This era of digital identity became the foundation upon which all public trust was built, ensuring that services remained accessible and secure for everyone. As these systems matured through the late 2020s, they proved that a centralized approach could balance the need for high-level security with the demand for a frictionless, modern user experience. Governments that embraced this evolution ultimately delivered more value to their taxpayers while safeguarding the digital lives of their citizens against an increasingly complex array of threats. Moving forward, the focus remained on refining these systems to ensure they stayed inclusive, transparent, and adaptable to whatever technological shifts appeared next on the horizon.